Every action now has
an agent behind it.
Classify human, trusted agent, or malicious in real time - and act before the request completes.


The new attack surface
Your defenses were built for humans.
Every fraud control you own - MFA, WAF, device checks, CAPTCHAs - assumes a person at the keyboard. Agentic AI breaks that assumption. Now software logs in, fills forms, and moves money on a user's behalf, and the line between a helpful assistant and an attacker is invisible to legacy tools.
Acting on a user's behalf
Browser agents click, log in, and check out using real credentials. To your stack it looks like a legitimate session - because it is one.
Attacks at machine speed
Credential stuffing, scraping, and synthetic onboarding now run thousands of perfectly-formed requests a minute - no fatigue, no mistakes.
High-risk actions automated
Refunds, account recovery, withdrawals, and profile changes are exactly the flows agents are pointed at - and exactly where abuse hurts most.
Prompt injection & shadow AI
Hijacked instructions and unmonitored no-code agents turn trusted automation into an exfiltration path you never provisioned.
~50%
of internet traffic is already automated - and agentic AI is accelerating the share.
0 of them
solve a CAPTCHA the way a human does - yet many now pass them anyway.
<50ms
is all you get to decide allow, step-up, or block - before the action completes.
How it works
Classify the agent behind every action
One continuous loop runs on every session - from first touch to the riskiest transaction.
01
Observe
Capture behavioral biometrics, device, and network signals on every session event - silently, with zero user friction.
02
Classify
Decide human, trusted agent, or malicious in real time - distinguishing helpful automation from an attacker.
03
Score
Maintain a continuous CARTA risk score across the whole session - not a one-time check at the door.
04
Act
Return a verdict in under 50ms so your app can allow, step-up, or block on your own rules.
Capabilities
One signal layer for the agentic era
Behavioral biometrics, device intelligence, and continuous risk scoring - purpose-tuned for software that behaves like a user.
Agent vs. human classification
Tell a real person, a declared trusted agent, and a malicious bot apart - on the same login, same device, same flow.
Behavioral biometrics
Keystroke rhythm, cursor entropy, scroll velocity, and touch dynamics - the human signals agents can’t fake.
Device & network intelligence
Continuous fingerprinting flags headless browsers, emulators, rotating identities, and impossible-velocity sessions.
Continuous (CARTA) risk scoring
Risk is re-evaluated on every event, not just at login - so a session that turns hostile is caught mid-flight.
High-risk action monitoring
Extra scrutiny on refunds, account recovery, withdrawals, and profile changes - the actions agents are pointed at.
Prompt-injection & abuse signals
Surface injected-instruction patterns, shadow-AI access, and automation abuse before they become an exfiltration path.
Live detection
Watch it classify in real time
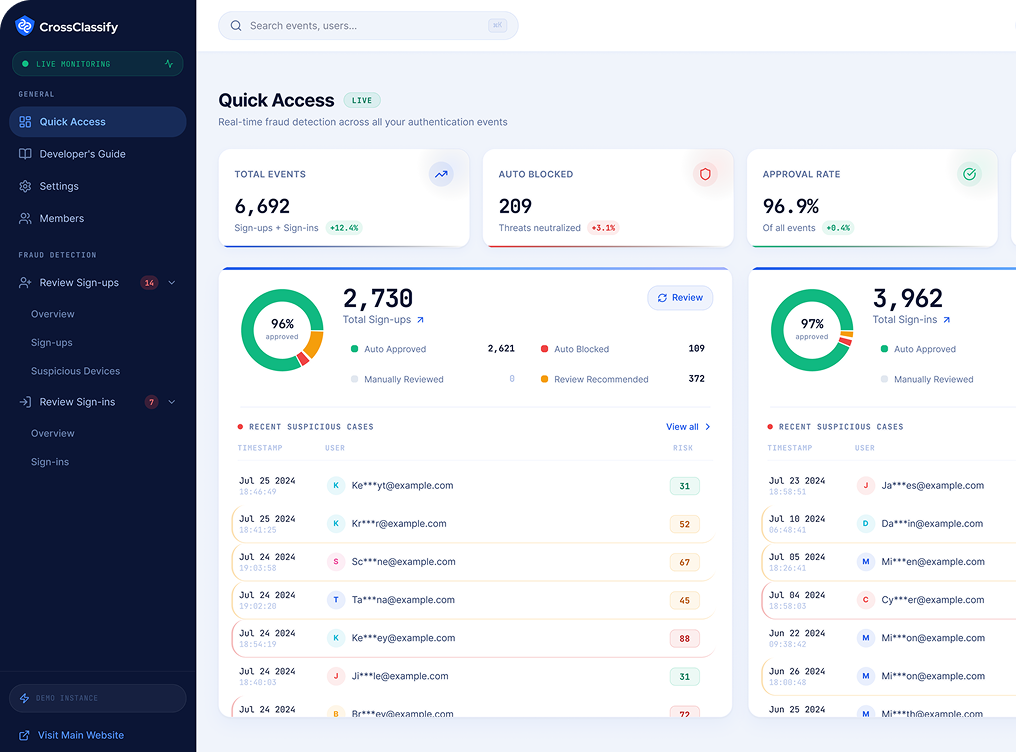
Every incoming session is scored against thousands of behavioral and device signals. Trusted agents and humans flow through; abuse is flagged before the action lands.
0
Allowed (human + trusted)
0
Auto-blocked
Agent stream · live
/v1/classify
Integration
One SDK. Up in minutes,
not days.
Drop in the SDK, send session events, and read a verdict on every action. No model training, no rules to hand-write on day one.
Edge verdict returned synchronously in under 50ms.
Your rules, your actions - allow, step-up, or block on your terms.
Explainable signals on every decision - no black box.
index.html
<body>
  <!-- Your existing content -->

  <!-- Add before closing body tag -->
  <script
    src="https://unpkg.com/@cross-classify/xc-sdk@latest/dist/xc-sdk.min.js"
  ></script>
  <script>
    CrossClassify.initXC(
      YOUR_SITE_ID,
      YOUR_API_KEY,
      {
        developerMode: true, // Enable for testing
        loginRoute: "/login", // Your login page path
        signupRoute: "/signup", // Your signup page path
      }
    );
  </script>
</body>
Why CrossClassify
Built for agents, not just bots
Legacy tools answer "is this a bot?" The real question is "which agent is this, and should it do this?"
| Capability | CAPTCHA | Bot management / WAF | CrossClassify |
|---|---|---|---|
| Distinguishes good agents from bad | |||
| Behavioral biometrics | Partial | ||
| Continuous scoring after login | Partial | ||
| No friction for real users | |||
| Detects agent acting for a user | |||
| Explainable, per-decision signals | Partial |
Frequently asked questions
Customer Stories
Trusted By Security Teams
We wanted better post-login fraud detection, but we didn't want to create another queue of alerts for our team. After adding CrossClassify, manual investigation time dropped by 58%, while we identified 4x suspicious sessions in the first six weeks that our existing controls hadn't surfaced.
58%
drop in manual investigation time
4x
more suspicious sessions identified
Nick Chang
COO, Helfie
Our concern wasn't whether we needed more visibility, we knew we did. It was whether getting it meant rebuilding the WAF and MFA setup we already had. CrossClassify was running alongside our existing stack in under 48 hours, and within the first month it surfaced 37 suspicious sessions we wanted our team to investigate.
<48h
to run alongside existing stack
37
suspicious sessions surfaced in month one

Dr Merran Cooper
CEO, Touchstone Life Care
We weren't debating whether we needed better visibility on our developer portal logins, that part was obvious. What held us back was assuming it meant standing up a whole new alerting pipeline for the team to babysit. CrossClassify slotted in without adding a single new queue, and it cut our team's manual login review time by 46% within the first three weeks.
46%
drop in manual login review time
3 weeks
to achieve the reduction
Anastas Manojlovski
CEO, Roast my IVR
We knew our enterprise SSO logins needed tighter monitoring, no argument there. The hesitation was purely about whether it meant rearchitecting how access works across Teams, WhatsApp, and email sharing. CrossClassify ran alongside our existing setup with zero changes to that flow, and over the following two months it surfaced 3x more suspicious sessions than our previous setup ever caught.
3x
more suspicious sessions surfaced
2 months
to measure the increase
Ali Najmi
CEO, SharePad
Let's Get Started
Create your free
account today
Discover how to secure your app against fraud using CrossClassify
No credit card required